

What it is
The remediation layer between vulnerability findings and production code
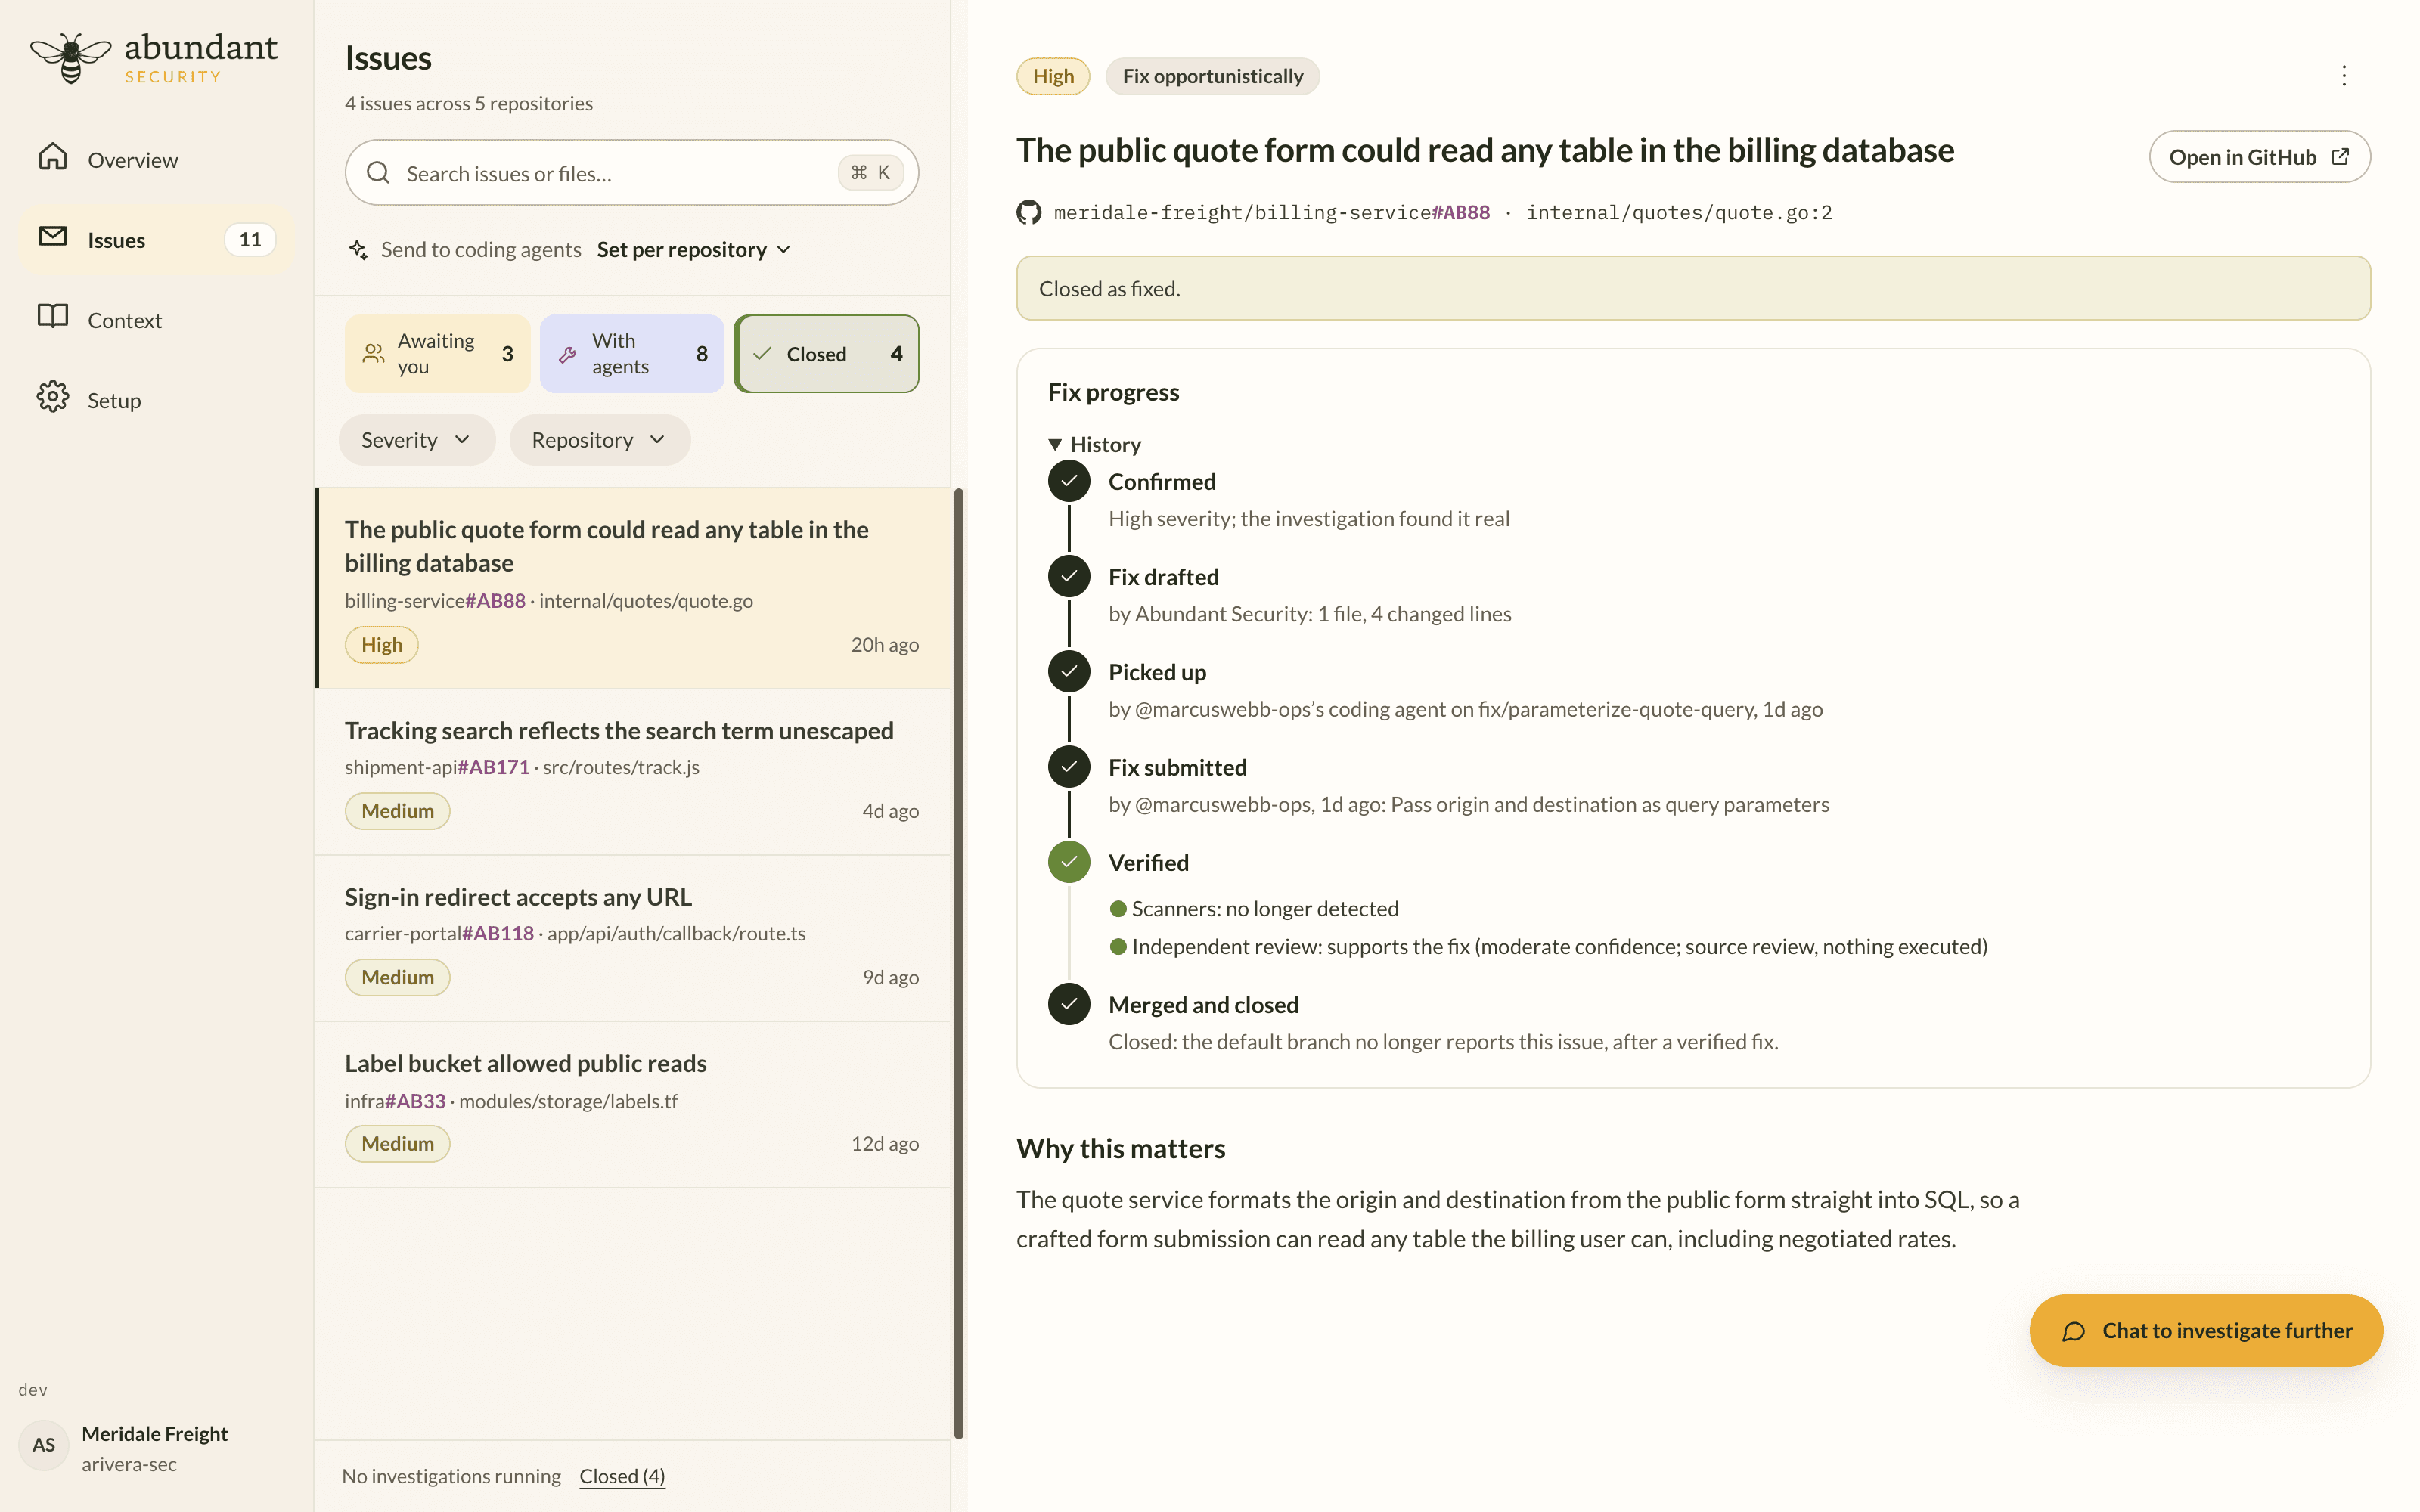
Send Abundant a vulnerability. Agents gather the context required to create a safe remediation plan, write and verify the fix, then deliver it through Claude Code and Codex.
What It Solves
FOR SECURITY ENGINEERS
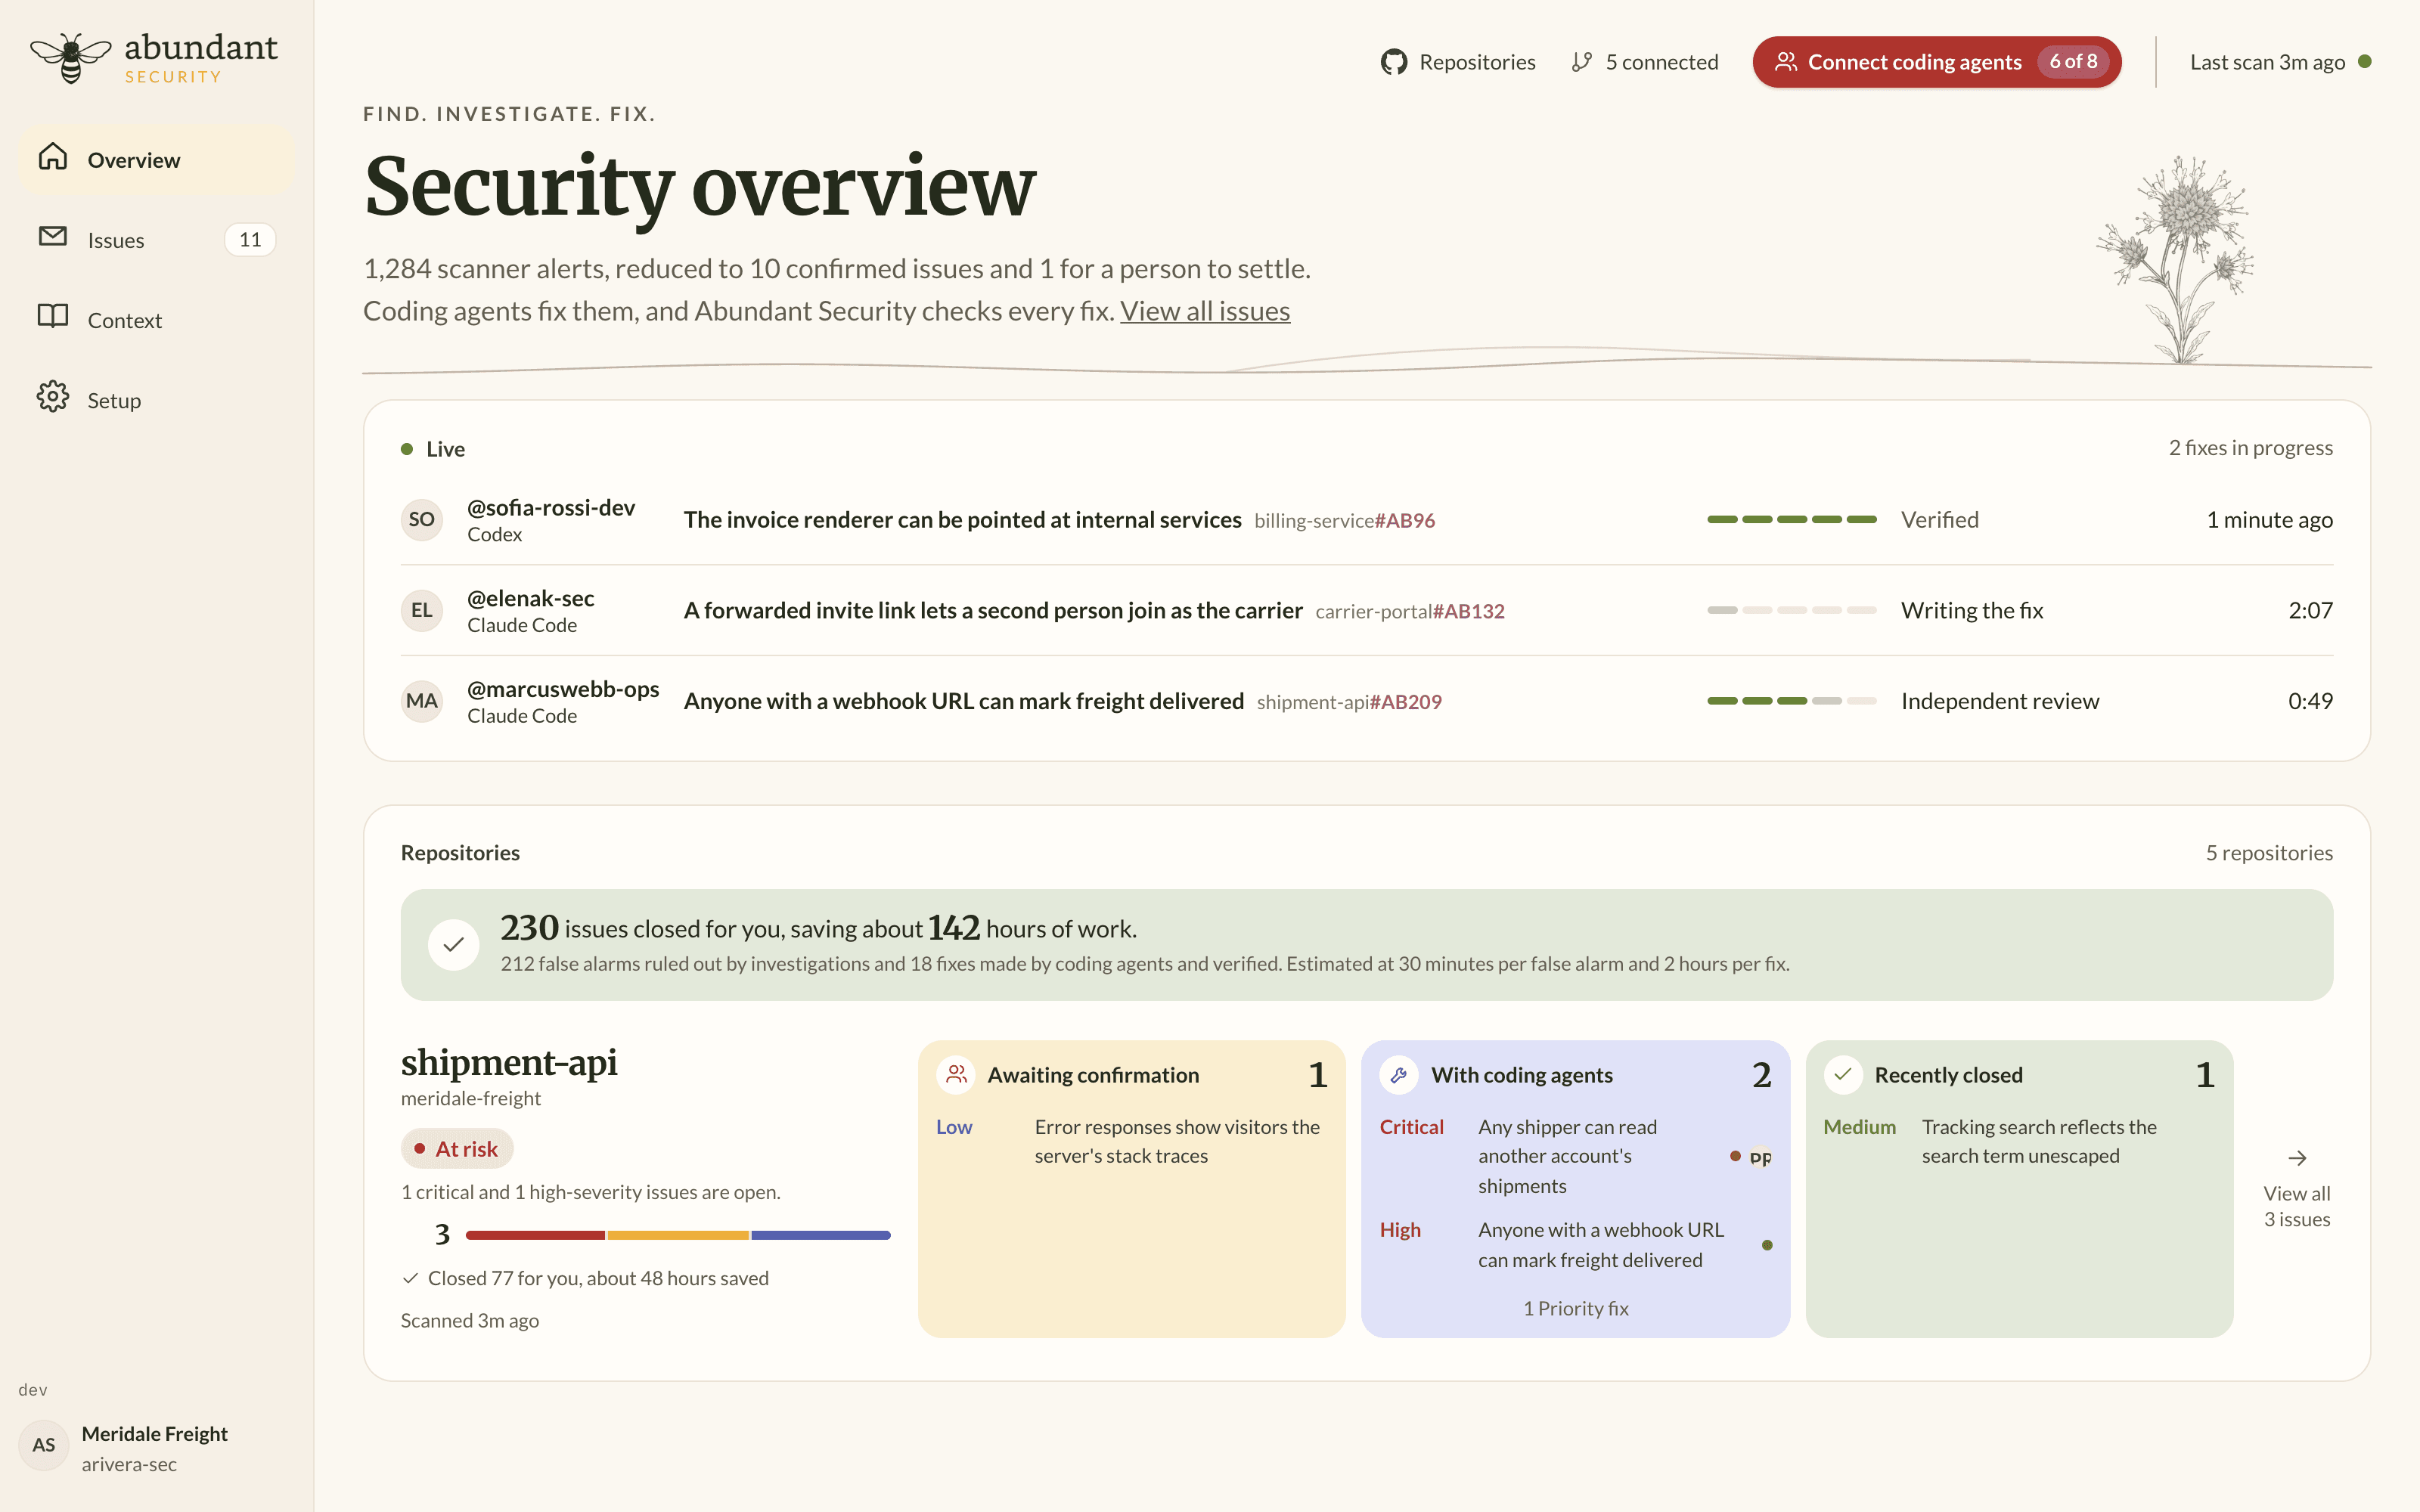
Stop handing raw vulnerabilities to engineering
Abundant takes the finding and gathers the code, reachability and application context required to create a safe remediation plan.
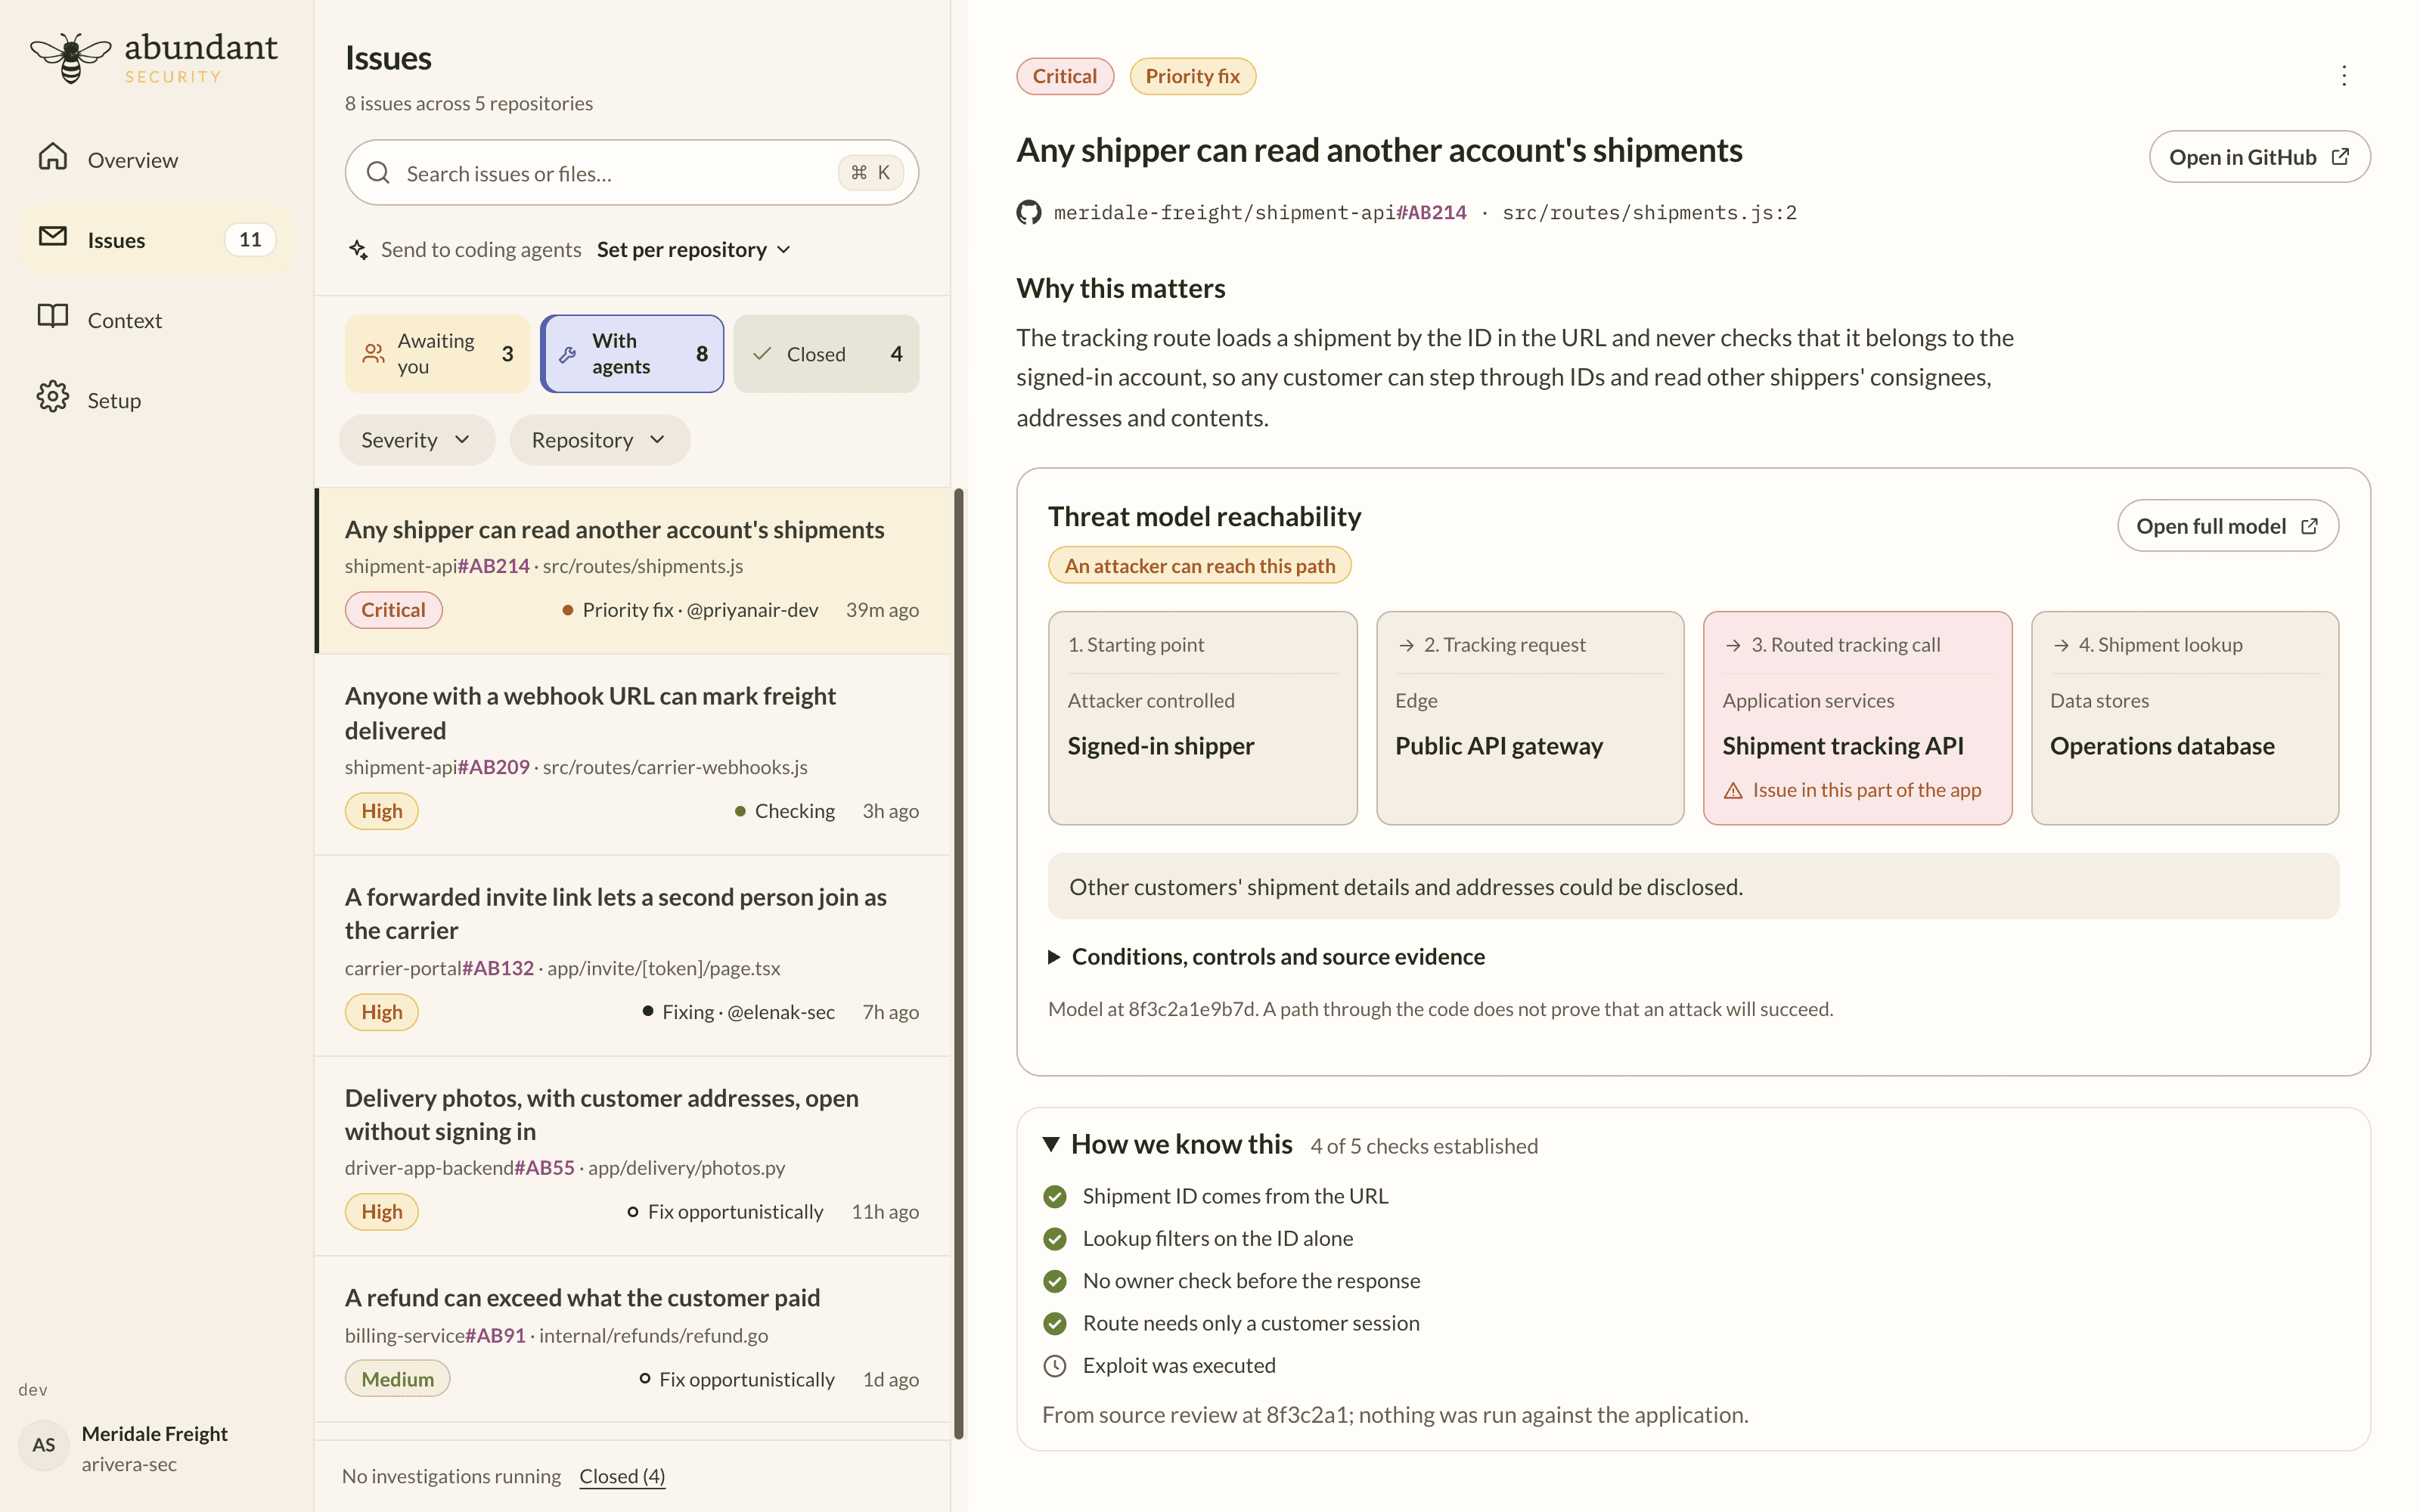
Route every fix to the right developer
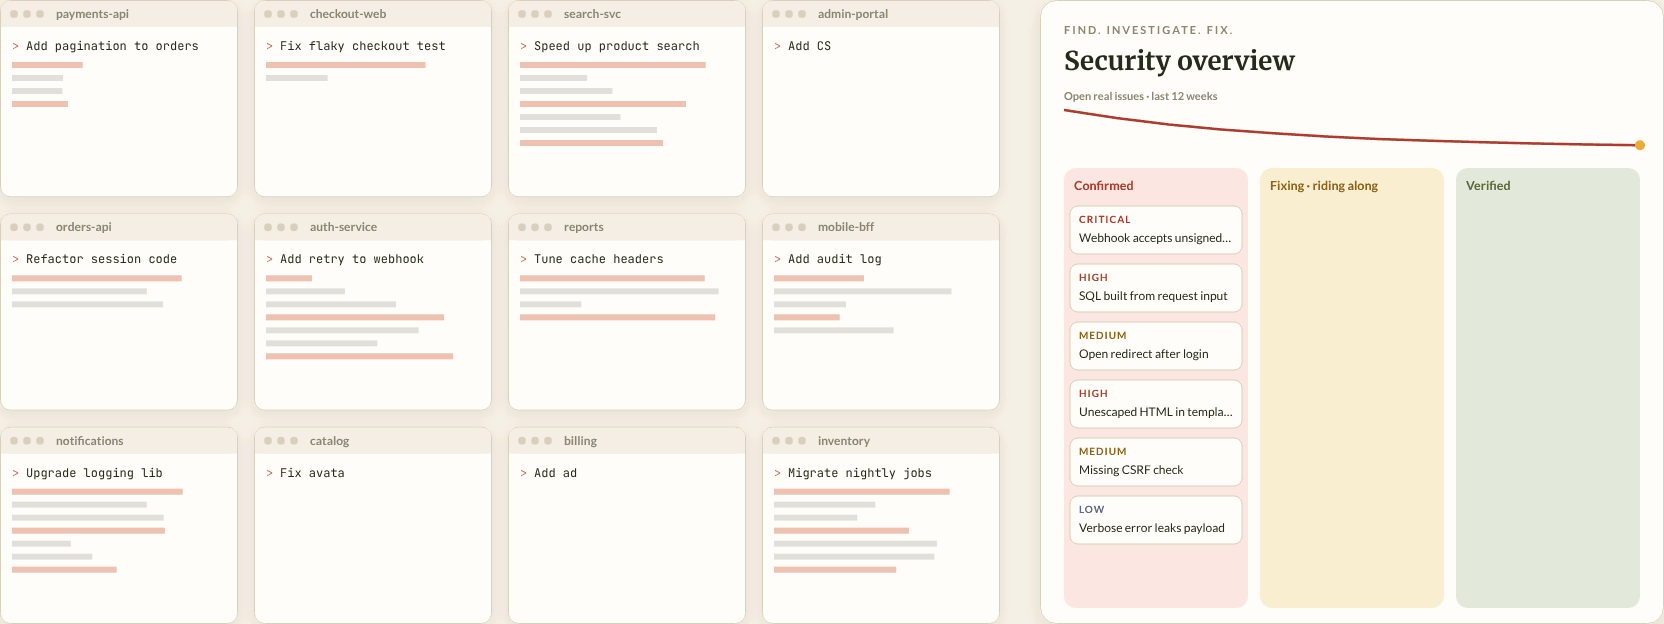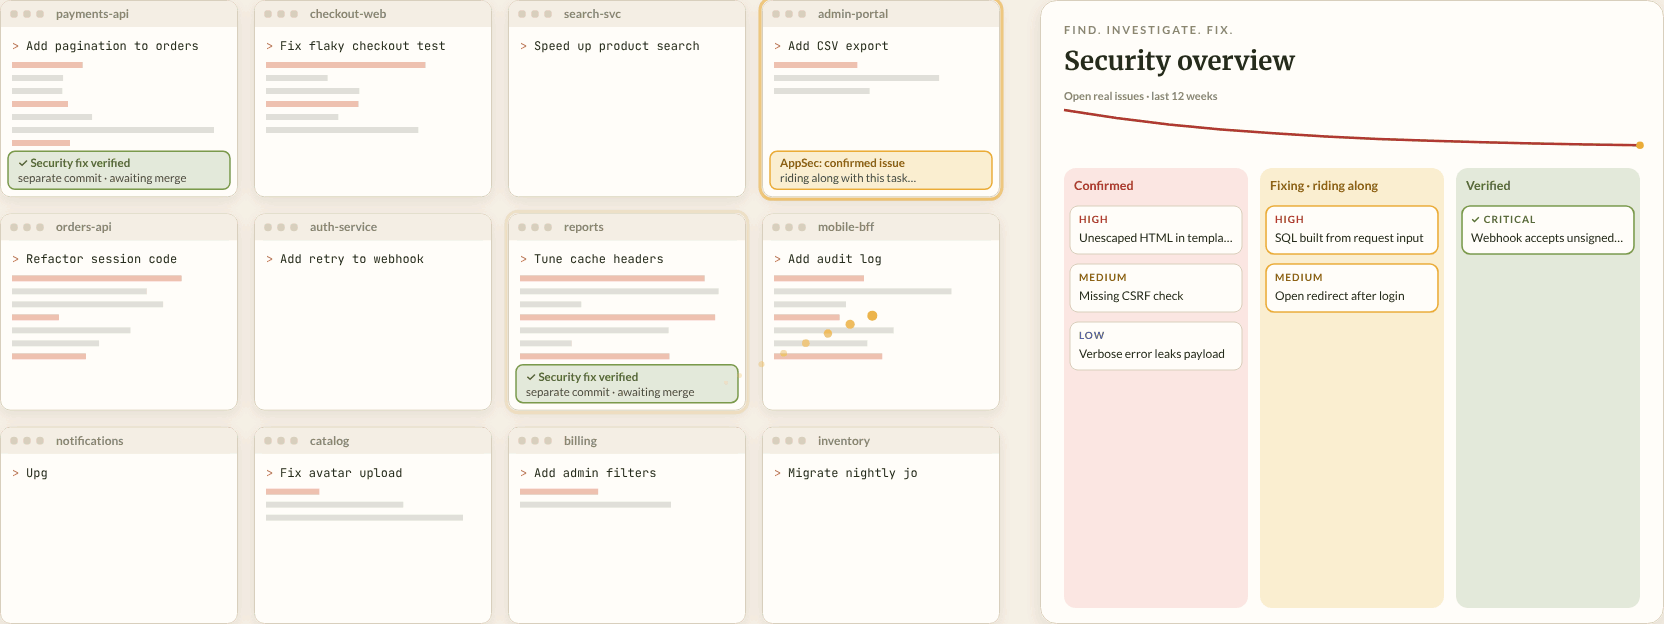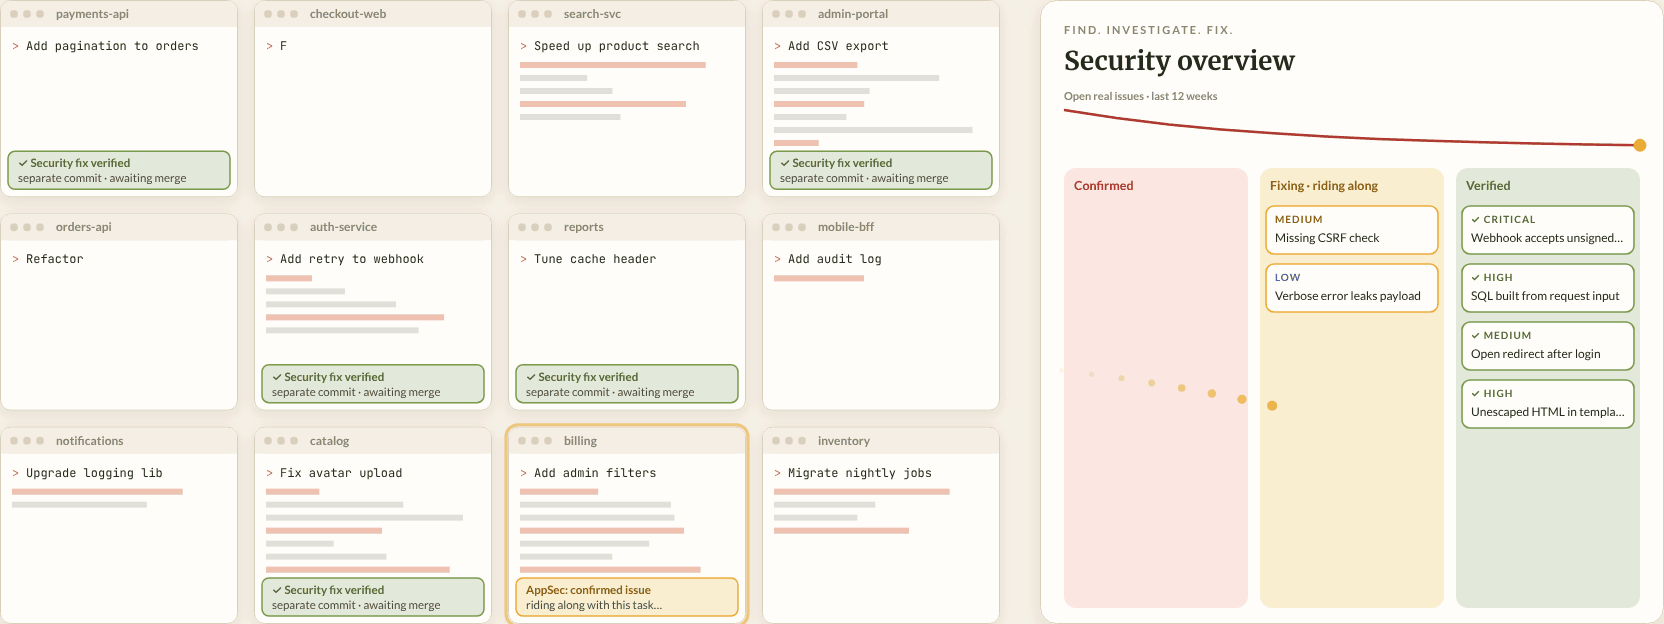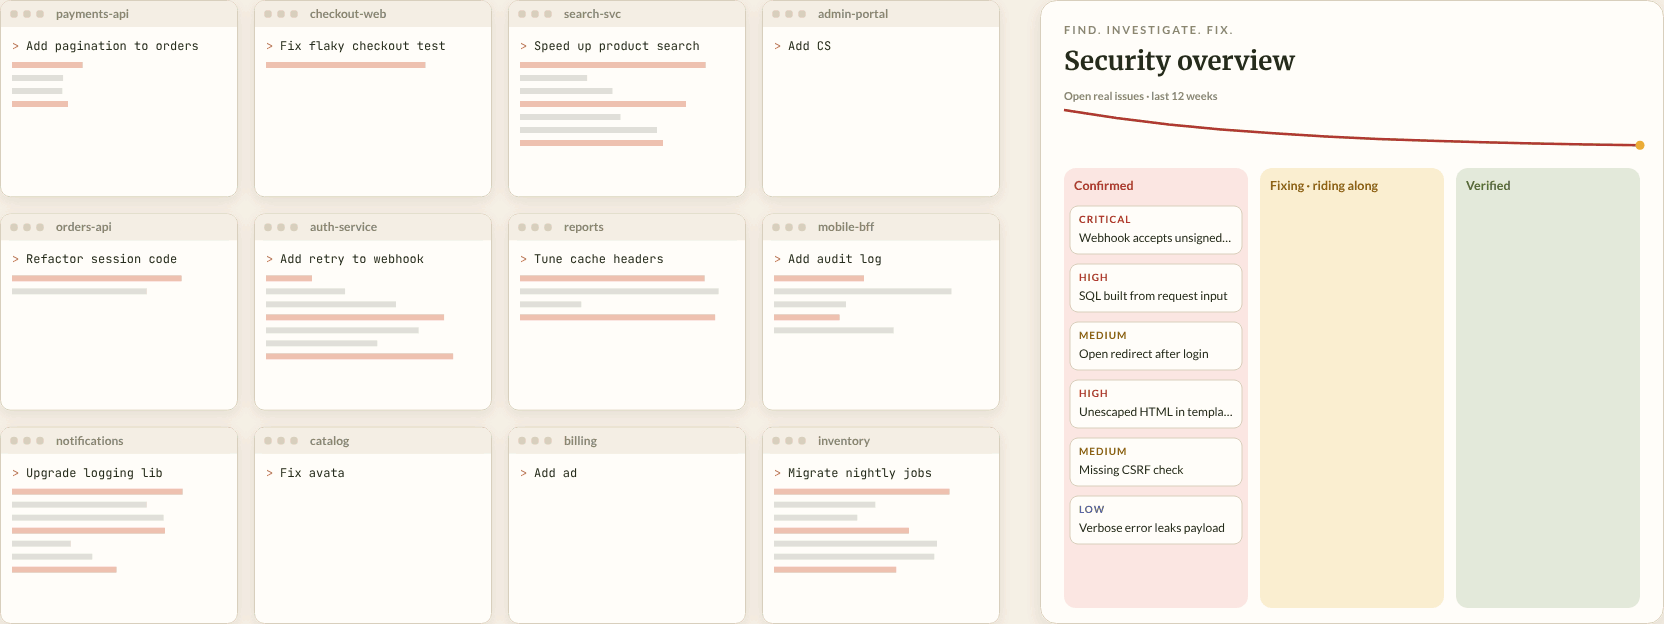
Abundant routes confirmed fixes into the right coding-agent session, where they ride along with everyday work and land as separate commits.
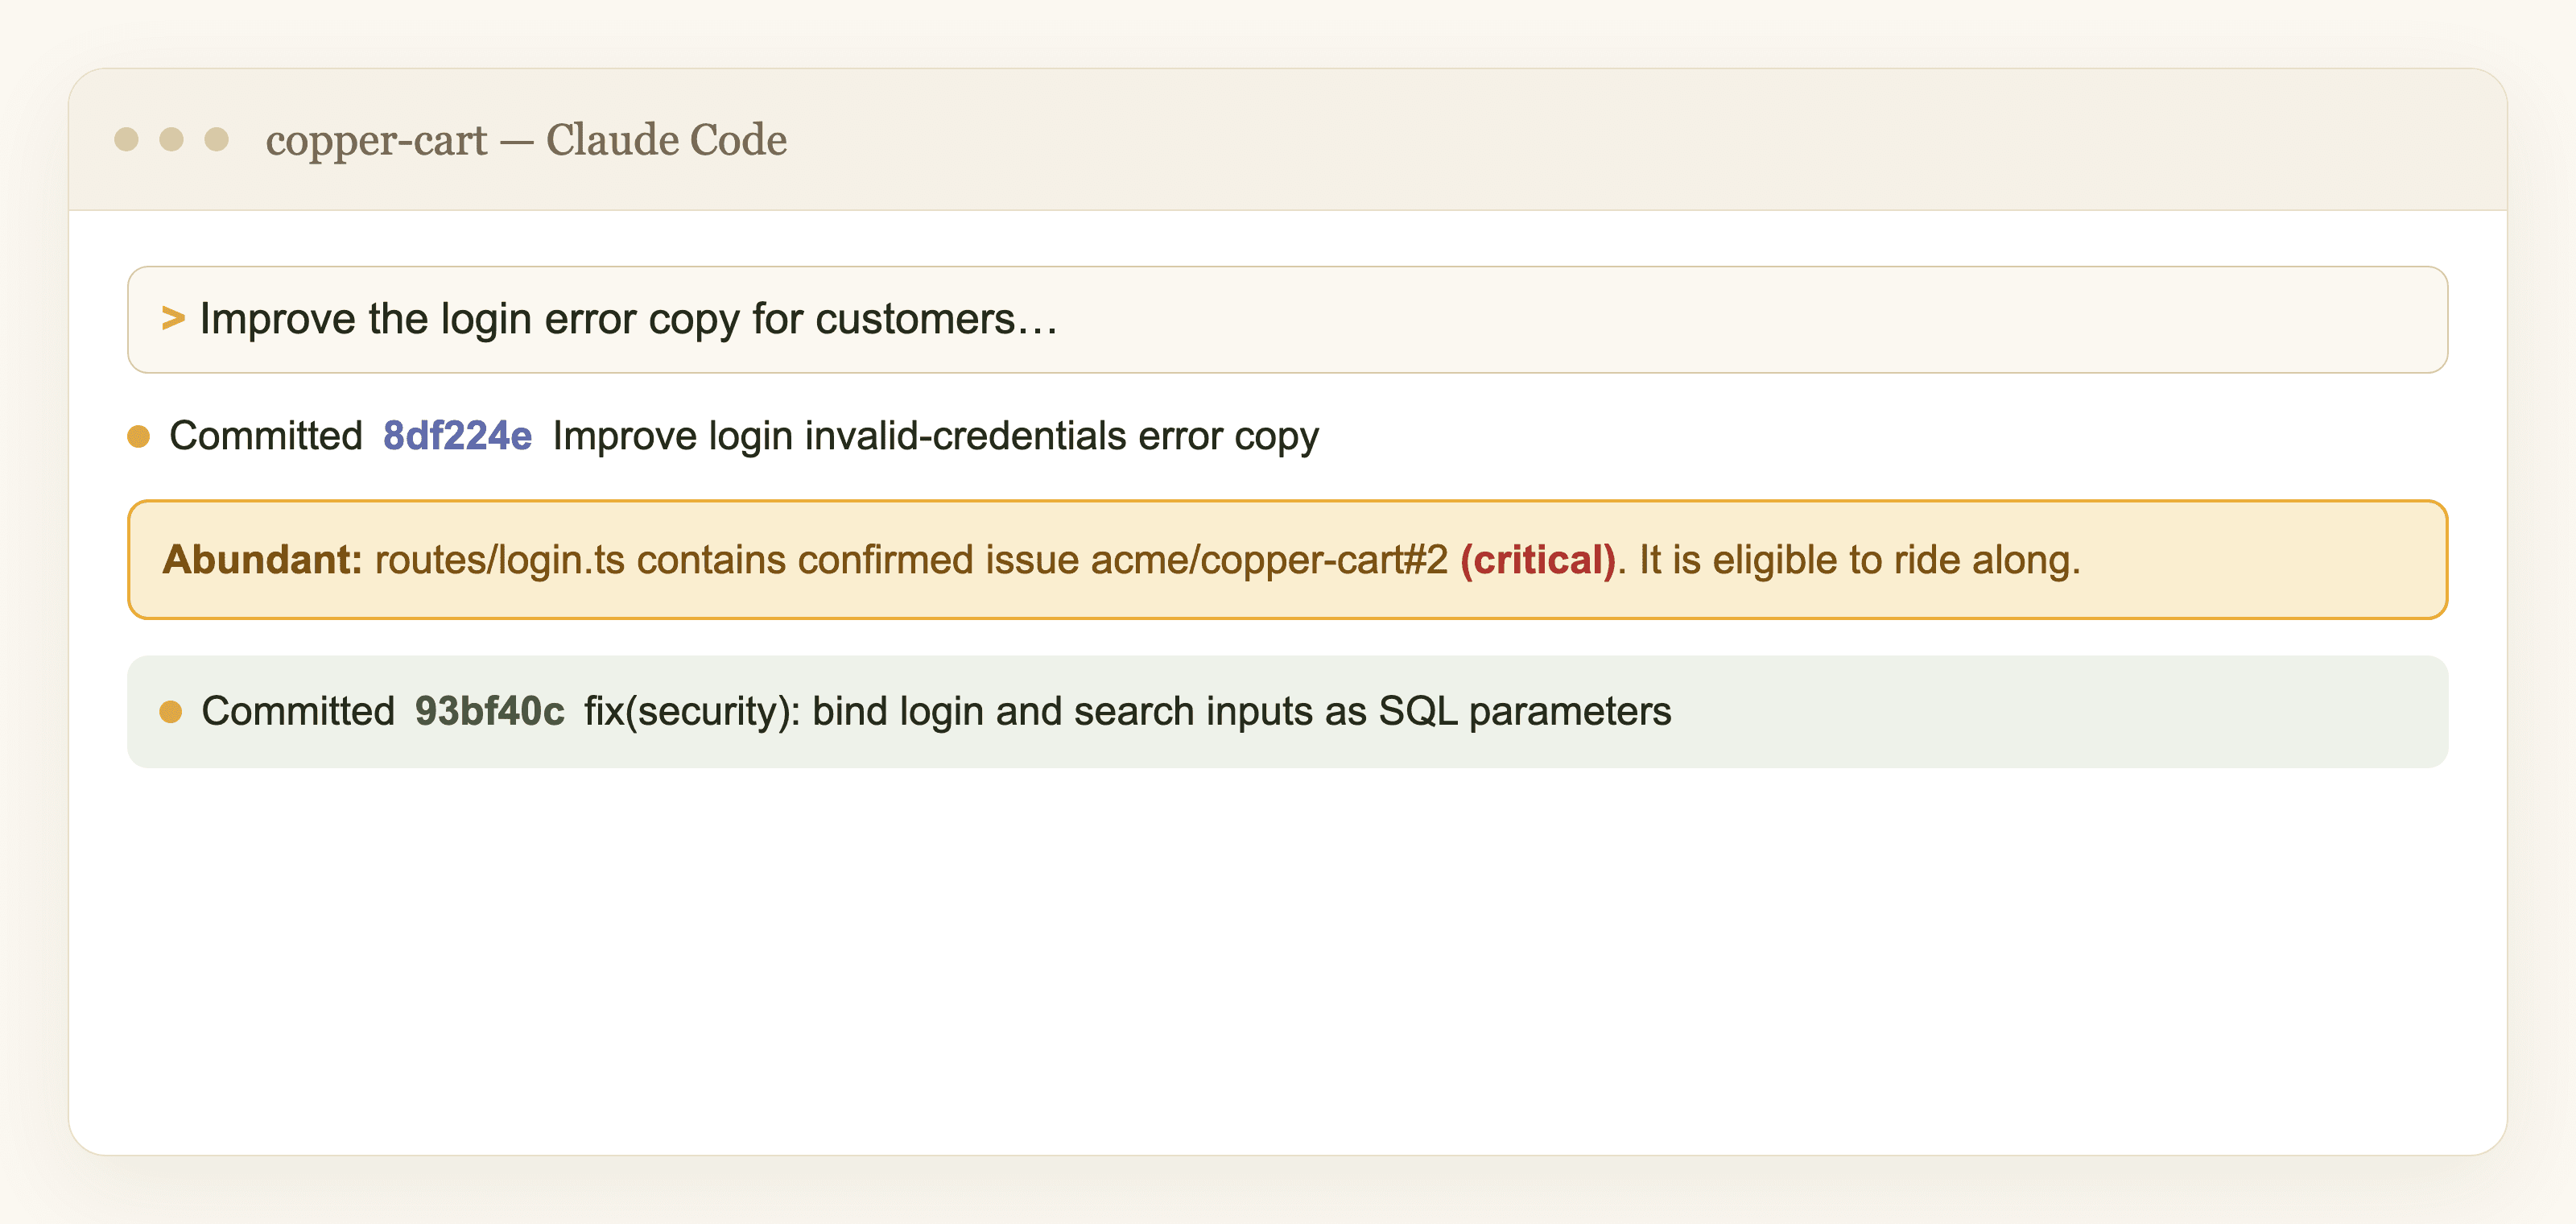
A fixing system, not another finding system
Abundant works from vulnerabilities found by your existing tools and drives each one toward a remediation plan and verified fix.
FOR CISOs
Show leadership what's actually getting fixed
Show leadership what's actually getting fixed: fixes shipped, vulnerability age, and where you're blocked.

It's not automated finding, it's automated fixing- CISO, Global Security Company
How it works
Security at machine speed, governed by humans.
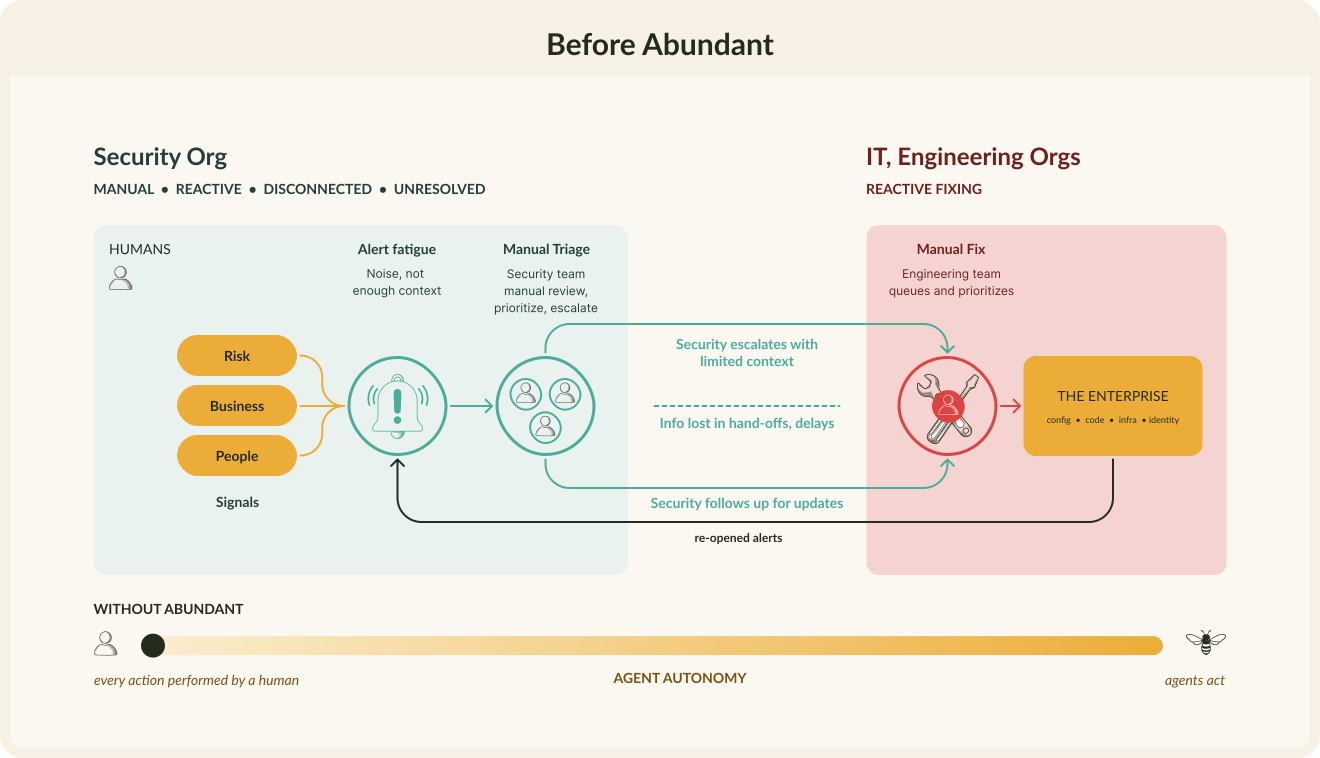
Security teams already have more findings than engineers can fix. Every vulnerability still needs investigation, code context, a remediation plan, ownership and a safe change.
The queue grows.
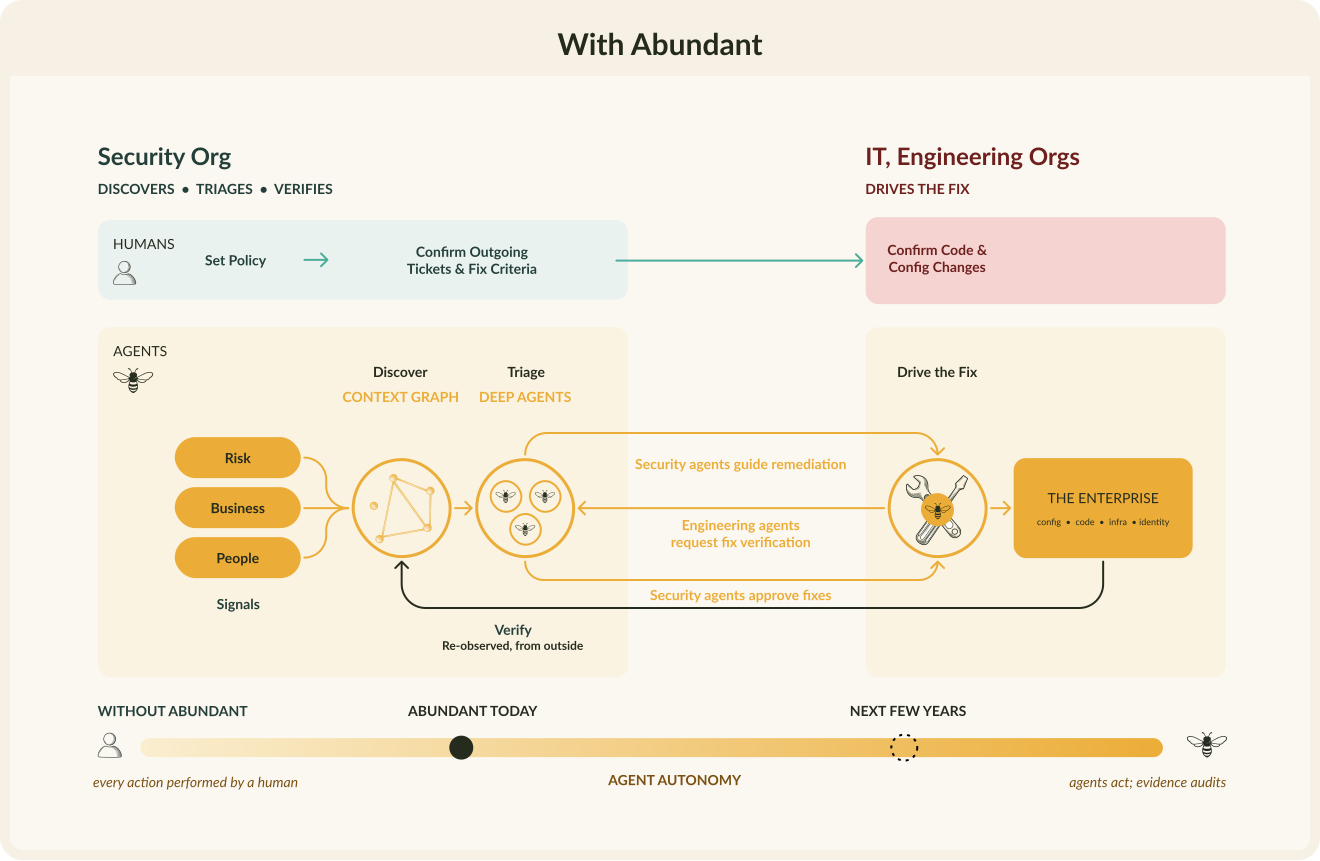
Abundant starts with the vulnerability. An investigator gathers the evidence needed to create the remediation plan, a fixer writes the change, and a separate verifier reviews it. The reviewed fix arrives through Claude Code and Codex, the agents engineers already use.
Automated fixing, not more findings.
For a decade this was the whiteboard fantasy, now it's here.

Agent Workforce
Investigator, fixer and verifier: separate agents, separate workspaces, one job — the fix.

Threat Model
Each repository's purpose, entry points, controls and attack paths ground every investigation. People can correct it, and their corrections stick.

Shared Memory
Every correction becomes a durable learning. An unchanged finding reuses its earlier verdict instead of being re-investigated.

Secure by Design
Your code runs only in a sandbox; the fixer and verifier never share a workspace; every GitHub write needs a person's approval.
